Everyone controls agent access. Only Rails controls their actions.
Agent policy-as-code to control what every agent can browse, spend, and deploy at runtime - before they act
By submitting this form, you agree to our Privacy Policy
30 day free trial. No credit card required. After trial, choose custom, annual, or monthly plan based on usage.
Trusted by Fortune 500s and industry leaders
Ungoverned or Stuck in Pilot?
Do you know what your agents did this morning?
What did your agent spend?
What did your agent browse?
Did your agent push code?
Where is the agent audit trail?
Half of AI deployment failures by 2030 will be caused by insufficient runtime enforcement
Source: Gartner Top Predictions for Data and Analytics in 2026
Transcend Agent ControlsTranscend Rails answers “can my agent do this, for this purpose, right now?”
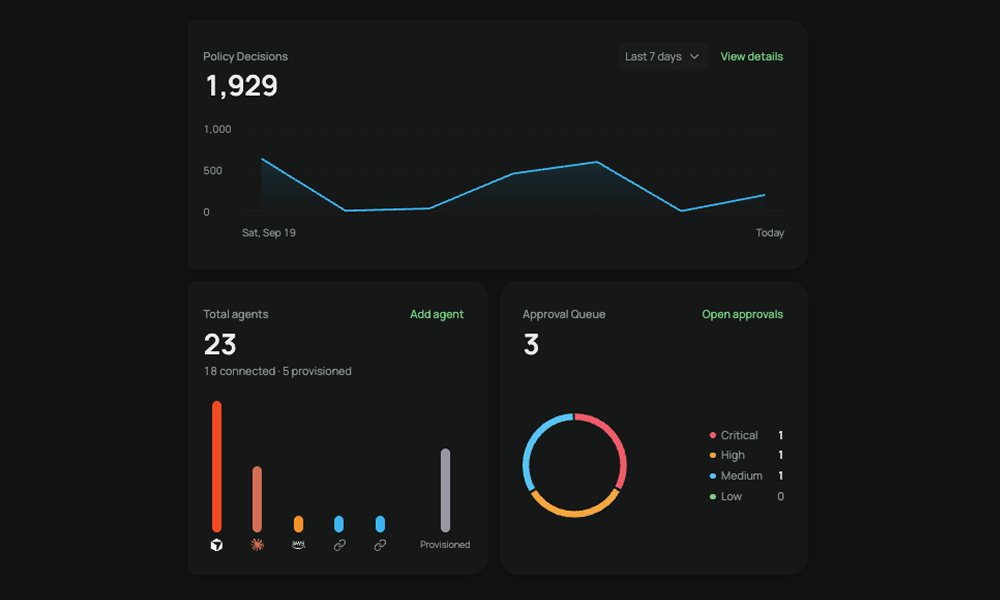
Transcend Rails is the agent policy-as-code platform that controls agents and everything they touch. Every action an agent proposes is checked at runtime and resolves to allow, deny or escalate before it happens.
Manage the sprawl
Ten agents, one set of rules on Rails. Adding the eleventh doesn't mean adding an eleventh version of them. Rails is built for enterprise complexity.
Get AI approved
A scheduling agent reads a medical appointment summary to book a follow-up. Only permissioned clinical data reaches the model. Rails never touches PII or your keys.
Give agents autonomy
A media company's CMS offered agents full write access or nothing. With one Rails policy, read but never write, editors now work with agents on live content.
Rails pays for itself. One customer saved 70% on token usage.
Customers measure Rails in multiple ways: agents moved from pilot to production, FTE time recovered, spend controls per agent, and revenue enabled. A customer’s CISO said the per-agent spend limits alone would pay for the platform.
By submitting this form, you agree to our Privacy Policy
“Transcend Rails gives each agent exactly the permissions and the budget its job needs, and nothing more. The ability to encode any business policy, with full ownership and auditability gives me the confidence to scale live agents across my tech stack. The spend controls alone pay for the platform.”
Jess Webster Francis
Associate Director, Cybersecurity, Privacy & AI Governance
THE AGENT MANAGEMENT PLATFORM IMPORTANCEWhat is Rails?
How it works
Your Agents on Rails
Agent control plane
Memory · Secrets
Decision API
Enforce + Audit
LLM providers
OpenAI, Bedrock
MCP servers
Slack, Notion
Web & APIs
Wikipedia, Salesforce
One MCP gateway is not sufficient. Rails has five enforcement points.
| Control point | Transcend |
|---|---|
Inference | Model calls: data use, model access, PII and prompt-injection checks on what goes in and what comes back |
MCP (Tools) | MCP tool calls and connectors: the specific operation on the specific resource |
Network | Web and API requests |
Memory | What the agent may retain and write back |
Secrets | API keys and credentials that your agent can use |
Rails works with internal & external agents across your tech stack
Amazon Bedrock AgentCore
Amazon Bedrock

Cortex AI


Adobe Experience Cloud
TRANSCEND Agent CONTROLS
Data privacy infrastructure, runtime agent action enforcement
Identity tools decide who an agent is. Gateways decide what it can reach. GRC tools document what it should do. Transcend Rails decides what the agent actually does, action by action, and can stop it before it happens.
One central policy decision point
Every agent, internal or third-party, calls one runtime decision point before it acts. We integrate with your identity providers (e.g. Okta, WorkOS) to import existing roles. Allow, deny, or escalate comes back.
MCP-native, stack agnostic
Covers Claude Desktop, Claude Code, Cursor, AWS Bedrock and AgentCore, Snowflake Cortex, Adobe Experience Platform, Databricks, and more. It speaks MCP with open-source SDKs, so there's no proprietary client and no data plane rewrite.
Policy as code, versioned and tested
Policies are written in plain language and translated into Rego with standardized versioning. Each new policy and update is simulated against real agent traffic before it rolls out. The enterprise baseline is inherited by every brand and use case.
Five control points, default fail-close
Inference, tool calls, network, memory and the secrets are all governed by the same policy set. Default fail-close (business can also write custom override). Low latency, P95 <75ms SLAs
Deployed in your VPC, secure data use cases
Decisions run inside your cloud through Sombra, Transcend's zero-trust gateway. Keys stay with you, including through your own KMS with HSM-backed management. Transcend never sees your data. Designed for the most sensitive data use cases.
Full-fidelity decision logs
Every decision is logged, with nothing sampled. Each record shows the agent, its owner, the rule, the policy version and the approver. A kill switch stops any agent on any stack, and an agent is quarantined when its owner leaves. Immutable, OTEL compatible audit trail.
the sombra differenceRuns in your environment, never touches your keys.
Rails runs through Sombra, our self-hosted, zero-trust gateway, inside your infrastructure. Your API keys stay with you, and every decision is applied under your security policies, on the same architecture the largest companies in the world already run for their customer data.

How much of your AI roadmap is stuck in the sandbox?
Bring us the agents your teams are already running. We'll show you what one policy would have allowed, blocked and escalated last week, in your own stack.
By submitting this form, you agree to our Privacy Policy.
Why your business needs Rails
Agent management maturity assessment
Take the 7-question Agent Management Maturity Assessment to see where your governance stands, where it falls behind agent deployment, and what to do next.
Agents on Rails Technical Whitepaper
A practical architecture for governing agent actions at runtime, so enterprises can move from sandboxed pilots to autonomous AI in production.
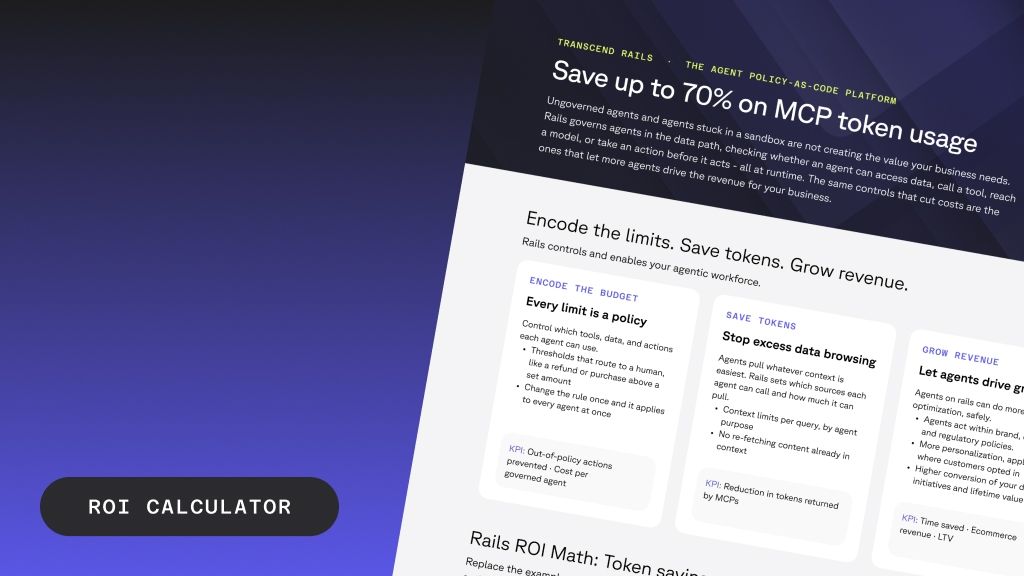
Rails Agent Management ROI
Turn agent governance into measurable ROI, from lower token costs to faster paths from POC to production.