agent management at scale
Control what your AI agents can do, before they act
Access control determines what your agents can reach. Transcend Rails goes further, enforcing policies on what each agent can do, for what purpose, and in real time - before an action happens.
Trusted by Fortune 500 brands and industry leaders. Gartner Magic Quadrant Leader in Privacy UX.
Rails governs agent actions across every tool
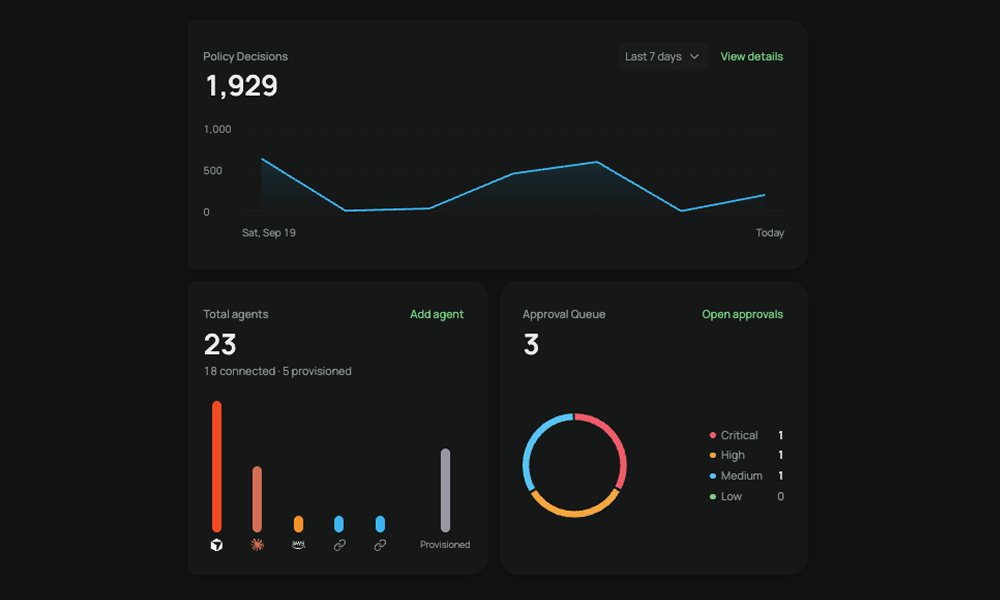
One policy across every tool below. Every action resolves to allow, deny or escalate before it runs, with the owner and the reason in the log.

A marketing agent can read customer data, but can’t send it to an outside vendor or use it in a model without consent.
Documentation defines the rules, but access control can’t enforce them once an agent is inside, and discovery only catches violations after the fact. Rails runs every action through the same checks before it happens: all allow and it runs, one deny and it stops.

Through 2028, at least 80% of unauthorized AI agent transactions will be caused by internal violations of enterprise policies.
Source: Gartner®, Market Guide for Guardian Agents, Avivah Litan, Daryl Plummer, Carlton Sapp, Dionisio Zumerle, Tom Coshow, Max Goss, Lauren Kornutick, 25 February 2026.
agents are evolving
Four things the agent control layer has to get right
Follow the agent across every system it touches
One task can run from Snowflake to HubSpot to LiveRamp, and each tool above sees one hop. The rule has to travel with the agent.
Check every action at every point it acts, not at one gate
Close one path and an agent takes another. Rails checks policy at inference, tools, network, memory and the decision itself.
Apply any rule the business can state as code
Read the ticket but never delete it. Refund under a limit. Business owners write the rule in plain language, engineers drop to Rego.
Give every agent an owner, a record and a kill switch
Every decision is logged with the owner, the reason and the policy version. When the board asks what your agents did, the answer is in the log.
“With Rails policy authoring, we can write controls as specific as our business needs. That's what got us comfortable connecting our agents to Shopify's MCP, which we'd held off on because the native controls weren't granular enough. On top of that, the spend policies are saving us tokens.”
Jess Webster Francis
Associate Director of Cybersecurity, Privacy & AI Governance, Dr. Squatch
How much of your AI roadmap is stuck in the sandbox?
Bring us the agents you already run and we'll walk through how one policy would apply to them, in your own stack.